
Malware injected into Rank Math PRO WordPress plugin in supply chain attack
Malicious code was inserted into packages of the paid Rank Math PRO plugin distributed from the vendor's site between October 15 and 16, planting backdoors on affected websites. The compromised period was approximately 11 hours, from 20:02 UTC on October 15 to 07:12 UTC on October 16.
Controls that address the technique described, from MITRE ATT&CK and NIST 800-53. They apply to the reader's own environment; the article does not say what the victim had in place, and this line makes no claim about it.M1051ATT&CK mitigation M1051
Update SoftwareM1016ATT&CK mitigation M1016
Vulnerability ScanningCM-07NIST 800-53 CM-07
Least FunctionalityCM-11NIST 800-53 CM-11
User-installed SoftwareSI-02NIST 800-53 SI-02
Flaw Remediation

ConnectWise disables Cloud Backup after attackers use compromised credentials to access Microsoft 365 tenants
Threat actors obtained a Microsoft 365 credential belonging to ConnectWise Cloud Backup and used it to gain unauthorized access to customer tenants; researchers identified at least 173 affected tenants. ConnectWise has suspended the Cloud Backup service and is conducting remediation, though the company has not confirmed the full scope of customer impact.
Controls that address the technique described, from MITRE ATT&CK and NIST 800-53. They apply to the reader's own environment; the article does not say what the victim had in place, and this line makes no claim about it.M1032ATT&CK mitigation M1032
Multi-factor AuthenticationM1018ATT&CK mitigation M1018
User Account ManagementM1030ATT&CK mitigation M1030
Network SegmentationCM-05NIST 800-53 CM-05
Access Restrictions for ChangeCM-06NIST 800-53 CM-06
Configuration SettingsCM-07NIST 800-53 CM-07
Least Functionality
Chinese espionage group exploited BeyondTrust zero-day since August
A China-linked group tracked as Armory Castle exploited CVE-2026-102764, a critical authentication bypass in BeyondTrust Remote Support versions 26.2.3 and earlier, for initial access in late August 2026. BeyondTrust has released patches for supported versions 24.3.1 and later; organizations on older versions lack available patches.
Controls that address the technique described, from MITRE ATT&CK and NIST 800-53. They apply to the reader's own environment; the article does not say what the victim had in place, and this line makes no claim about it.M1048ATT&CK mitigation M1048
Application Isolation and SandboxingM1030ATT&CK mitigation M1030
Network SegmentationM1016ATT&CK mitigation M1016
Vulnerability ScanningCM-05NIST 800-53 CM-05
Access Restrictions for ChangeCM-06NIST 800-53 CM-06
Configuration SettingsCM-07NIST 800-53 CM-07
Least Functionality
Proofpoint to acquire Varonis Systems for $6.3 billion in all-cash deal
Thoma Bravo-owned Proofpoint announced it will acquire Varonis Systems for $6.3 billion in an all-cash transaction. Varonis will become a private company following the deal.

Candiru spyware infected Al Jazeera devices through ordinary online ads without user interaction
Citizen Lab researchers found that the Israeli spyware vendor Candiru delivered zero-click infections to devices at Al Jazeera through targeted digital ads. The Record reports the spyware has infected devices worldwide through ads, though the accounts do not specify the full scope of targets beyond Al Jazeera or confirm whether the worldwide infections also involved Candiru.
Controls that address the technique described, from MITRE ATT&CK and NIST 800-53. They apply to the reader's own environment; the article does not say what the victim had in place, and this line makes no claim about it.M1056ATT&CK mitigation M1056
Pre-compromise
UK Legal Aid Agency says hackers stole records from 1978 onward in April breach
The Legal Aid Agency, which administers Britain's public defense service, disclosed that attackers who compromised its systems in April 2025 took records spanning nearly five decades. The agency's initial disclosures did not specify how far back the stolen data extended.
Microsoft disrupts phishing kits behind billion-message scam campaign
Microsoft and a coalition including Cloudflare, Proofpoint, and others shut down three phishing kits responsible for over 1 billion scam messages, with involvement from the Japan Cybercrime Control Center and Health-ISAC. One account reports the operation used a malicious traffic distribution system run by a Russian organization and abused thousands of Cloudflare links.
OpenAI employee arrested after hidden recording device found in conference room
Abdulrahman Alfozan, a Saudi national employed by OpenAI, was arrested Friday after the company discovered a hidden recording device in an executive conference room at its San Francisco offices. OpenAI referred the matter to the FBI and terminated Alfozan's employment.
DOJ charges 14 people, seizes laptops in operation against North Korean remote worker scheme
The U.S. Department of Justice charged 14 people and seized approximately 187 laptops from more than 40 locations in Texas in September as part of an operation against a scheme in which North Korean IT workers use remote access to hide their location and generate revenue for the regime, netting an estimated $3 million. The Record reports two arrests; The Hacker News states 14 people were charged, a mix of U.S. citizens and Chinese nationals, though the specific breakdown is not provided in the available text.
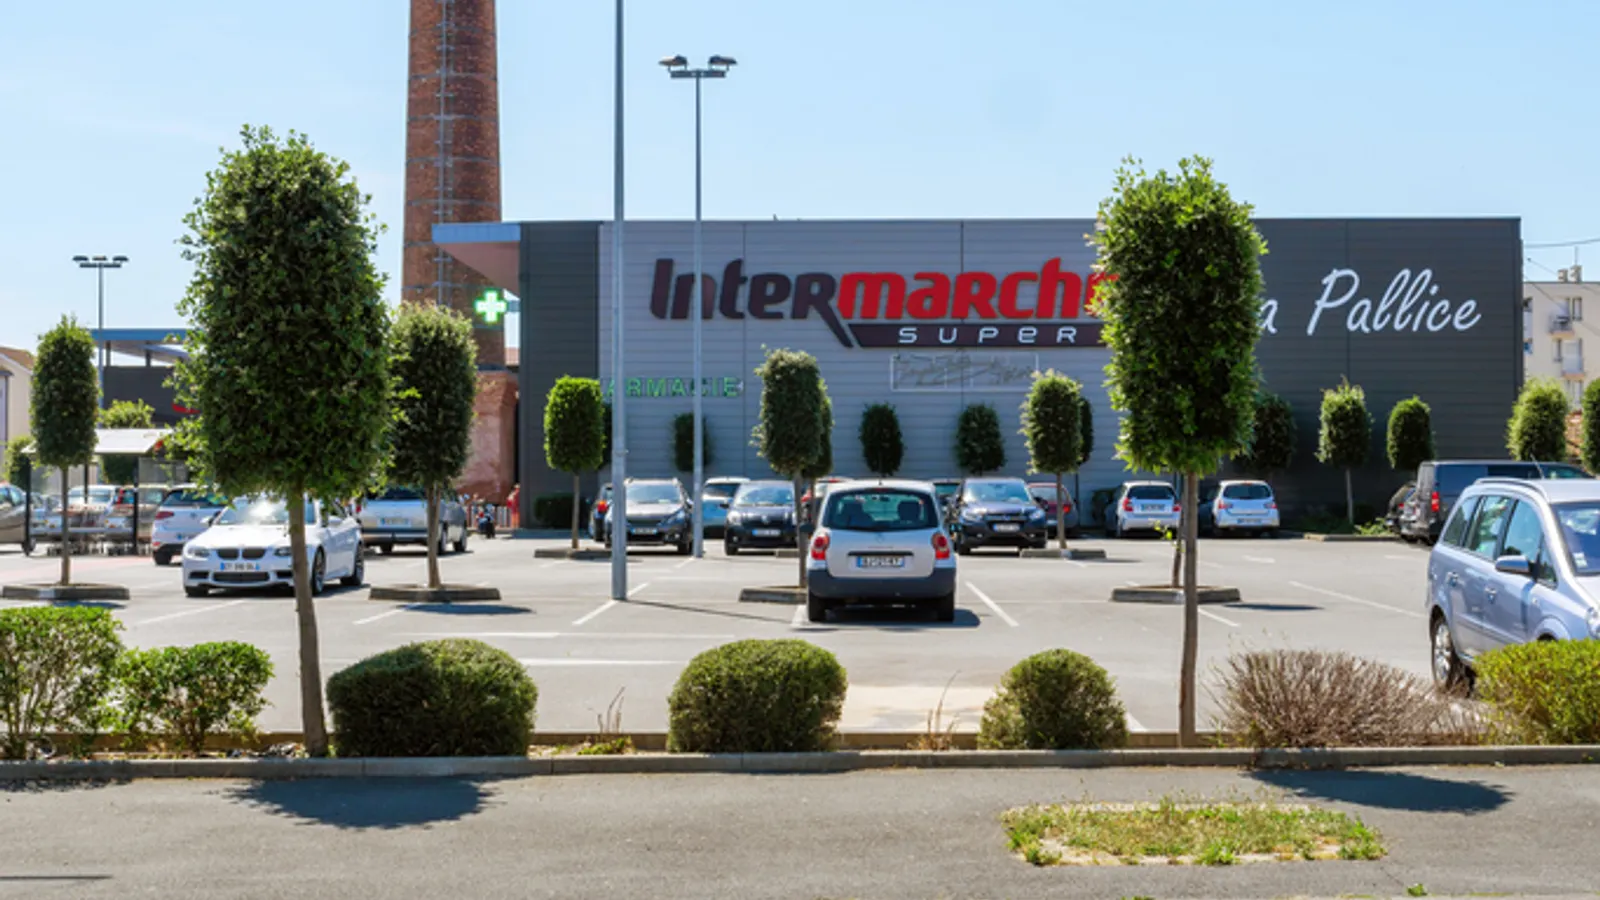
Supermarket refrigeration systems hacked across multiple manufacturers
Refrigeration equipment from Copeland and Dixell was hacked in attacks on retail locations, according to France's cybersecurity agency. The flaws exploited in the attacks had been disclosed months before the incidents occurred, but were not patched due to inadequate cybersecurity measures.
Ahold Delhaize takes systems offline after cyberattack affecting U.S. and European grocery brands
Ahold Delhaize confirmed a cyberattack forced it to disconnect systems across its U.S. and European operations, taking down websites for Food Lion, Stop & Shop, Hannaford, and other banners. Reuters reported the company stated it has no indication client data was stolen, though The Record notes the incident involved "malicious actions."

Ledger halts sales in Asia after discovering hardware implants in wallets
Ledger paused sales through resellers in seven Asian countries after finding unauthorized circuit boards implanted under device screens that exfiltrated user data; the tampering was linked to an $86 million cryptocurrency theft. The company is investigating the supply-chain attack but the accounts do not specify which resellers were compromised, how many devices were affected, or whether implants have been found in devices sold through other channels.

Attackers remotely heated refrigeration controllers at French supermarkets, spoiling food worth millions
Attackers gained remote access to Danfoss refrigeration controllers at hundreds of French supermarket locations on October 11, raising temperatures to 50°C (120°F) and forcing stores to discard spoiled food. The accounts do not specify how the attackers obtained access to the controllers or whether other countries besides France were affected.
Controls that address the technique described, from MITRE ATT&CK and NIST 800-53. They apply to the reader's own environment; the article does not say what the victim had in place, and this line makes no claim about it.M1048ATT&CK mitigation M1048
Application Isolation and SandboxingM1030ATT&CK mitigation M1030
Network SegmentationM1016ATT&CK mitigation M1016
Vulnerability ScanningCM-05NIST 800-53 CM-05
Access Restrictions for ChangeCM-06NIST 800-53 CM-06
Configuration SettingsCM-07NIST 800-53 CM-07
Least Functionality

Hackers hijack AOMEI update servers to secretly spread malware
Exploited Fortinet Bug Linked to Stealthy FortiGate Implant in Telecom Hack

A hacker broke into John Deere and SharkNinja with an army of AI agents

Nikkei discloses third data breach in a month, 1.8M records exposed

One Compromised Login Exposed Millions of California Students’ Records

OpenCode Console Breach May Have Exposed OpenAI, Anthropic, and Google API Keys

Hackers steal customer data from major Russian hosting provider FirstVDS
